

What are sandbox images?
Sandbox images are pre-configured container images that serve as blueprints for creating sandboxes. Each image includes:- Base environment: Operating system and runtime configurations
- Tools: Languages, frameworks, and development tools
- Configuration: Environment variables, startup scripts, …
- Resources: Memory allocated
How sandbox images work
- Initial setup: Follow this guide to create your sandbox image for the first time. Use
bl pushto publish the image to Blaxel’s registry without creating a new sandbox or affecting existing sandboxes, orbl deployto push the image and also create a sandbox from it. - Build phase: Your Dockerfile is used to create a container with all required tools and configurations. Blaxel then slims the image, removing files that are usually only needed at build time.
- Initialization phase: The sandbox API is injected and startup commands are executed.
- Instantiation: New sandboxes can be spawned from this image in seconds.
You cannot directly use “library” container images (such as those hosted on Docker Hub and other registries) as sandbox images. Instead, you must create one or more custom images for your sandboxes using Dockerfiles and ensure that each image includes Blaxel’s sandbox API binary. This is necessary for sandbox functionality like process management and file operations.
Pre-built images
Blaxel provides a library of pre-built container images for common needs.Custom images
You can also customize an image for specific needs.Create a sandbox image
You can create a customized sandbox image using the Blaxel CLI or REST API.Blaxel CLI
1. Initialize an image
Start by creating a new sandbox image using the Blaxel CLI:2. Customize the Dockerfile
The Dockerfile is the heart of your image. It defines what will be available in your sandbox environment.3. Configure image settings
Theblaxel.toml file defines your image’s runtime configuration:
Variables set here apply to every sandbox created from this image. On the new sandbox generation, you can also update variables on a running sandbox or give them a new value when you fork a sandbox. See the variables and secrets documentation for details.
4. Define initialization
Theentrypoint.sh script runs when a sandbox is created from this image:
5. Build and test locally
Before pushing the image to Blaxel, test it locally:6. Push the image
Once satisfied with your configuration, push the image to Blaxel:- Build your Docker image
- Push it to Blaxel’s registry (private to your workspace)
- Return an image ID you can use for creating sandboxes
Blaxel SDK
The Blaxel SDK includes a declarative image builder that lets you define custom sandbox images directly in your code using a fluent, chainable API. Instead of writing Dockerfiles manually, you describe your image step by step, and the SDK generates the Dockerfile, builds the image, and deploys it as a sandbox. This approach is ideal for dynamic image definitions, CI/CD pipelines, or when your image configuration depends on runtime logic.The declarative image builder is available in the TypeScript and Python SDKs. The Go SDK does not support this feature.
- Define: Use the fluent API to describe your image starting from a base image.
- Chain: Each method returns a new immutable
ImageInstance, so you can branch and reuse configurations. - Build: Call
build()to generate a Dockerfile, package it with any local files, upload it to Blaxel, and deploy it as a sandbox.
Select a base image
Start by selecting a base image from any Docker registry:Execute build commands
Execute shell commands during the image build:Use package managers
The SDK provides convenience methods for common package managers. These generate optimizedRUN commands with sensible defaults (e.g., cache cleanup for apt).
Python (pip)
Python (uv)
Node.js (npm, yarn, pnpm, bun)
Install system packages (apt, apk)
Use other package managers
Add Dockerfile instructions
All standard Dockerfile instructions are available as methods.Specify the working directory
Define environment variables
Copy files
Expose ports
Set an entrypoint
Add users
Add labels and build arguments
Add local files
Copy files and directories from your local machine into the image:COPY-ed into the image. You can optionally provide a contextName (TypeScript) / context_name (Python) parameter to control the filename in the build context.
Build and deploy
Basic build
Build with all options
build() method automatically:
- Injects the Blaxel sandbox API binary
- Sets a default entrypoint if none was specified
- Packages the Dockerfile and local files into a ZIP archive
- Uploads and deploys the image as a sandbox
- Runs the default image slimming pass after the Docker build
- Polls until the sandbox reaches
DEPLOYEDorFAILEDstatus
Inspect the generated Dockerfile
You can preview the Dockerfile without building:Write to disk
You can also write the image to a folder for manual inspection or use withbl deploy:
Size the build environment
Large images can run out of memory or disk while they build. SetbuildMemory and buildVolume (build_memory and build_volume in Python) on build() to size the temporary environment the image is built in. These are the same settings as bl push --memory and --volume, or [build].memoryMb and [build].volumeMb in blaxel.toml.
When you omit them, the platform defaults apply. They only affect the build. The deployed sandbox uses
memory.
These options require
@blaxel/core 0.3.28 or later, or blaxel 0.4.16 or later. HIPAA workspaces do not support buildVolume; omit it or set it to 0.Understand immutability and branching
Each method returns a newImageInstance, leaving the original unchanged. This lets you create base images and branch from them:
Example script
A complete example building a Node.js / Python development sandbox:API reference
Methods
Properties
Blaxel API
Although less common, it is also possible to create a sandbox image and sandbox by directly interacting with the Blaxel API. Ensure that you have the following:- A Blaxel API key
- The workspace name, found at the bottom left corner of the Blaxel Console or via
bl workspaces
1. Create a ZIP archive
Create a directory with the following project contents:Dockerfile(required) - Defines your custom sandbox image and must includesandbox-api- Any custom scripts (e.g.,
entrypoint.shfor initialization logic) - Configuration files or data files as needed
- Additional dependencies or binaries your sandbox requires
- The Dockerfile is the heart of your image. It defines what will be available in your sandbox environment. See an example.
- The
entrypoint.shscript runs when a sandbox is created from this image. See an example.
2. Create a sandbox resource
Set your Blaxel API key and workspace as environment variables:upload=true query parameter in the request, which indicates intent to upload custom code.
The Blaxel API returns a JSON response. The response contains an x-blaxel-upload-url response header, containing the target URL to use when uploading your image. The URL is in the response headers, not the JSON body.
Example response:
3. Upload ZIP archive
Use an HTTP PUT request to upload the ZIP file to the upload URL. Replace the placeholder URL in the command below with the value of thex-blaxel-upload-url response header received earlier.
200 OK status code.
4. Monitor deployment status
After uploading, poll the sandbox status endpoint to track the build and deployment progress. Make a GET request tohttps://api.blaxel.ai/v0/sandboxes/<SANDBOX-NAME>, where SANDBOX-NAME is the metadata.name specified in the initial POST request.
status field of the response will progress through these values:
See sandbox deployment statuses for the full list of statuses a sandbox can report outside of this initial deployment flow.
Continue polling every 3-5 seconds until the status reaches
DEPLOYED or FAILED.
A first sandbox from that image is automatically created on Blaxel once deployment succeeds. You can safely delete the sandbox and keep using the image for new sandboxes.
Example script
Here’s a complete example script that performs all the steps above:mytemplate with your custom Dockerfile and entrypoint script:
deploy-sandbox.sh (Shell), index.ts (TypeScript) or main.py (Python):
Deploy from a private registry
Instead of building from source, you can pointblaxel.toml directly at an image in a private registry:
bl push or bl deploy as usual.
To configure registry credentials, you have three options (listed in priority order):
-
Pass the credentials inline to
bl pushorbl deploywith the--registry-credflag -
Pass the credentials from a different configuration file to
bl pushorbl deploywith the--docker-configflag -
Place a
.docker/config.jsonin your project directory using the standard Docker config format (you can copy your existing~/.docker/config.json). The file will be automatically detected and used bybl pushorbl deploy.
- Docker Hub
- GitHub Container Registry
- Google Artifact Registry
- Amazon ECR
- Any private registry which supports Basic auth
Use a custom image
Once an image is successfully pushed, you can spawn new sandboxes instantly by using its image ID. Use the following command to retrieve the image ID of the most recently pushed image:Run the workload as a non-root user
Everything in a sandbox runs asroot by default. To scope processes, terminals and filesystem operations to an unprivileged user while the sandbox API keeps the privileges it needs, declare the user in your Dockerfile and enable the feature:
Update a custom image
To update an existing custom image:- Modify your Dockerfile or configuration
- Rebuild locally to test changes
- Push the new version:
Image slimming
After the Docker build finishes, Blaxel runs a slimming pass on the image root filesystem. The pass reduces image size and sandbox boot time. It removes a fixed list of paths that are typically only needed while the image is building:- package manager caches
- documentation and man pages
- headers and static libraries
- systemd
- Python
__pycache__directories - build toolchains, including
make,gcc,g++,cmake,autoconf, andautomake
RUN instructions can still use these tools while the image is building. The tools are absent when a sandbox starts from the published image.
bl push and bl deploy run this pass. Local docker build and make run keep the filesystem Docker produced. A binary can exist in that local container and be missing from the sandbox. The SDK build() method uploads the image to the same pipeline, so the pass runs there too.
Slimming is enabled by default. For images you publish with bl push or bl deploy, disable it in blaxel.toml when the running sandbox needs a compiler or another build tool:
slim = false, the image keeps caches, documentation, headers, and build tools. The image is larger. Sandboxes take longer to boot. Leave slimming enabled when those files are only needed to compile dependencies during the image build.
Clean up unused images
Use the Blaxel Console to delete unused image tags in bulk and free image storage. This is useful after repeated builds or when you approach your total image-size quota. Check your account’s limits on the Quotas page. Cleanup applies to the selected workspace, across resource types, not only sandbox images. Image tags referenced by existing resources are kept, including those used by sandboxes on standby. Unused tags can be deleted even when another tag of the same image is still in use. To clean up images:- Open the Blaxel Console and select the workspace you want to clean up.
- In the sidebar, open Sandboxes > Images. Review the images and their Total size values.
- Click Cleanup Unused to open the Cleanup Unused Images dialog.
- Review the warning and type
cleanupin the confirmation field. - Click Cleanup Images to delete unused image tags.
Share images across workspaces and accounts
Once you have a custom image, you can share it with other workspaces in the same account, or with other accounts - for example, to promote an image fromdevelopment to production without rebuilding or re-pushing, or to share an image between different teams. Only the metadata record is copied to the target workspace or account; the underlying storage stays in the source.
When you share an image:
- The metadata is copied to the target workspace or account, pointing to the same underlying data in the source.
- The target workspace or account can use the shared image to create sandboxes, just like a locally-owned image.
- Storage billing stays with the source workspace or account.
- New tags pushed to the source image are automatically propagated to all workspaces and accounts it is shared with.
sourceWorkspace field. In the Blaxel Console, they are marked with a badge showing the source workspace or account name.
Prerequisites
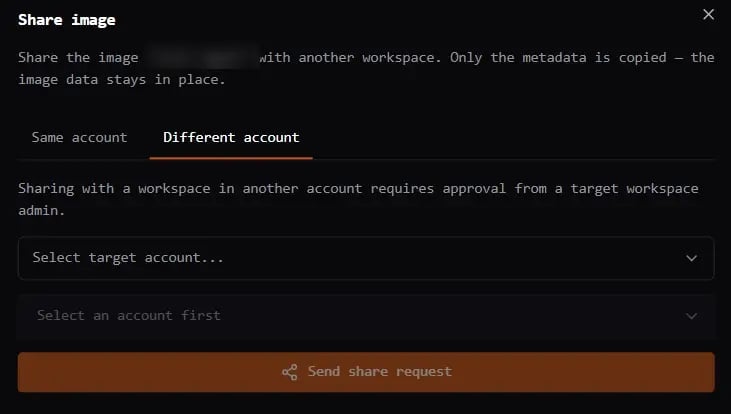
- When sharing between workspaces or accounts, you must be an administrator of the source workspace. When sharing between accounts, your share request will be completed only when it receives approval from an administrator of the target account.
- The image must be locally owned in the source workspace or account. You cannot re-share an image that was shared to you from elsewhere.
Share an image
Blaxel Console
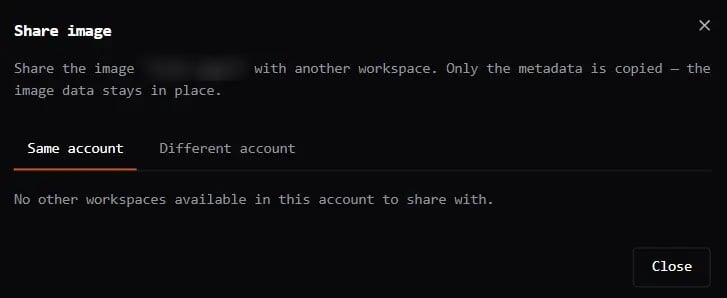
To share with another workspace in the same account:- Navigate to the Images page in the source workspace.
- Click the actions menu (three dots) on the image you want to share.
- Select Share.
- In the dialog, select the Same account tab.
- Select the target workspace from the dropdown.
-
Click Share to confirm.
- Navigate to the Images page in the source workspace.
- Click the actions menu (three dots) on the image you want to share.
- Select Share.
- In the dialog, select the Different account tab.
- Select the target account from the dropdown.
-
Click Share to confirm.
Blaxel CLI
Currently, the Blaxel CLI only supports image sharing across workspaces. To share images across accounts, use the Blaxel Console or the Management API instead.
bl share image command:
Sharing applies to the entire image (all tags). Tag-qualified references like
sandbox/my-template:v1.0 are not accepted.Management API
For sharing between workspaces in the same account:List shared images
Blaxel Console
On the image detail page in the Blaxel Console, images shared across workspaces or accounts are listed with the option to revoke sharing for each workspace or account individually.Management API
Unshare an image
Unsharing removes the metadata record from the target workspace or account. The image data in the source workspace is not affected. You cannot delete an image (or individual tags) while it is shared. You must unshare from all connected workspaces or accounts first.Blaxel Console
- Navigate to the Images page in the source workspace.
- Open the image detail page.
- In the shared workspaces list, click Unshare next to the target workspace or account you want to revoke.
Blaxel CLI
Use thebl unshare image command:
Management API
Billing
Storage billing is tied to the source workspace. Metering and costs remain with the workspace that originally pushed the image, regardless of how many workspaces or accounts it is shared with. The consuming workspace or account pays nothing for image storage of shared images.Constraints and limitations
- No re-sharing: A shared image cannot be re-shared from the consuming workspace to a third workspace or account. Only the original owner can share.
- Deletion protection: You cannot delete an image (or individual tags) while it is shared with other workspaces or accounts. You must unshare from all target workspaces first.
- Whole image only: Sharing applies to the entire image with all its tags. You cannot share individual tags.
- Admin-only: Both sharing and unsharing require administrator permissions.
Best practices
1. Optimize for cold starts
- Use smaller base images (Alpine when possible)
- Minimize layers in Dockerfile
- Pre-install only essential packages
- Defer optional installations to runtime
- Leave image slimming enabled unless the sandbox needs build tools at runtime
2. Cache dependencies
3. Security considerations
- Don’t include secrets in images
- Use Blaxel’s secrets management for sensitive data
- Keep base images updated
- Scan for vulnerabilities regularly
4. Resource optimization
Choose appropriate resources for your use case:Volume templates
Pre-populate volumes with files for faster environment setup.
Workspace access control
Understand accounts, workspaces, and admin permissions.